Star system · Systems & networks
Pipeto
A security audit of a nuclear-reactor console full of planted vulnerabilities: find them, rank them, patch them and prove the fixes with tests.
- Orbit period
- Apr 2025 – May 2025
- Role
- Auditor and patch author
- Crew
- 2 people
- Status
- archived
Spectral lines
Pipeto Console is a pretend control program for a nuclear reactor: start it, read the temperature, adjust the power, simulate a meltdown. It is also a trap: the school wrote it with planted security holes, and the job was to act as the security team that finds them, writes them up and fixes them. No real reactor was harmed. Done with Samuel Bègue.
How it works
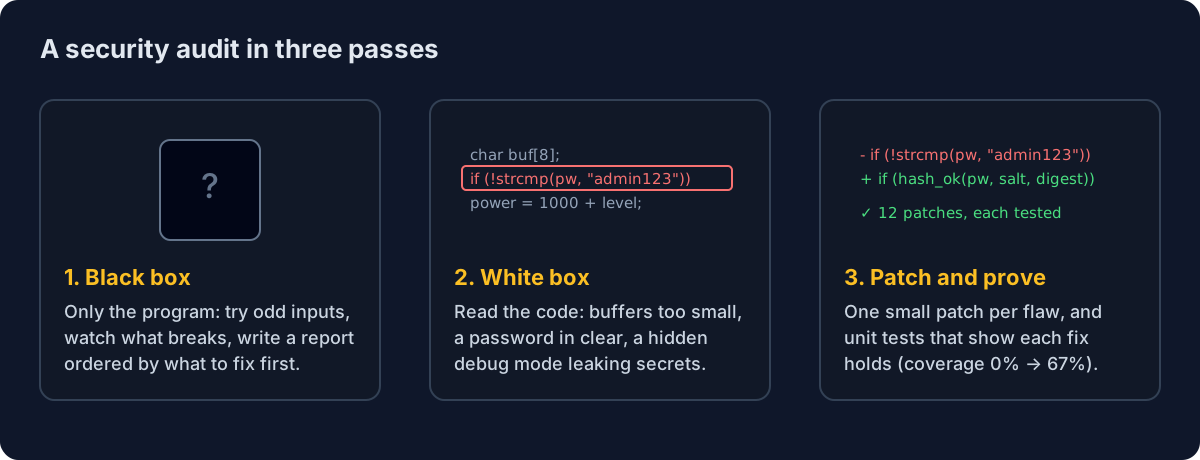
The audit had three stages. First from the outside, with only the program: try unexpected inputs and write a report ordered by what to fix first. Then from the inside, reading the code: buffers that are too small, a password written in clear, a hidden debug mode that leaked secrets. Finally fix and prove it: one small patch per problem, and tests that show each fix holds.
What I took from it
- A security report is only useful if it says what to fix first.
- The most dangerous bugs here were one-line mistakes, which is why each patch is tiny and each has a test.
Crew
- Samuel Bègue@Infamous97440No bio yet.GitHub